Information security as part of Tiva Safe’s history
Part of Tiva Safe’s association with information security comes from a responsibility undertaken during Solar Hijri years 1390–1394. Under a direct contract with the Kerman Provincial Governorate, the scope covered information security and technical support for the websites and web platforms of 169 executive bodies in the province at that time, including the governorate and municipality. Real-time monitoring, backups and round-the-clock support formed part of that engagement. The contract period has ended; the figure of 169 and the continuous coverage describe this historical work. Its relevance to our work today lies in understanding the responsibility that accompanies software on which an organisation’s daily operations depend.
Resilience starts with clear operational decisions
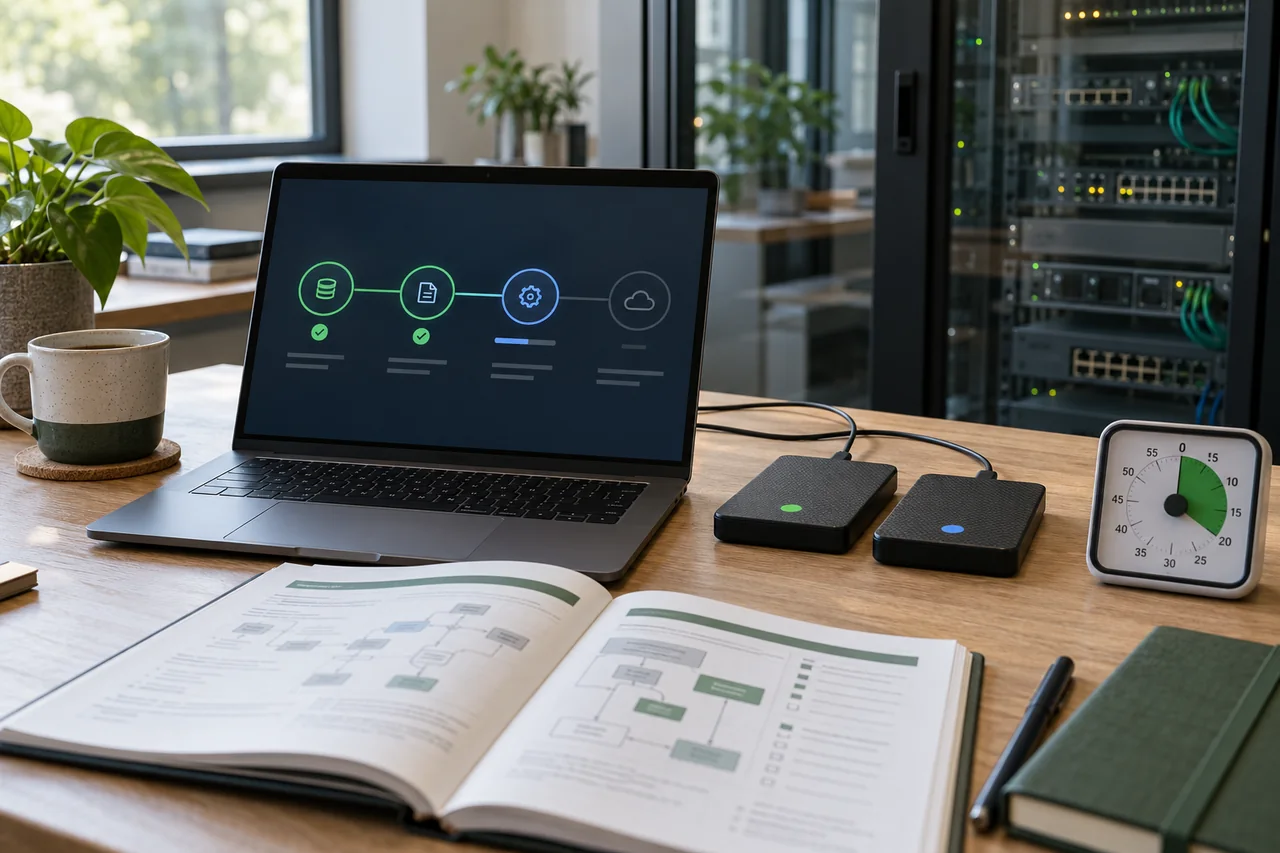
Infrastructure experience brings an important question into software design: if part of a system becomes unavailable, what should be restored first? The answer begins with the impact on the organisation and leads to essential data, dependencies and the person responsible for responding. Possessing a backup file is insufficient; the restoration process needs to be checked in a separate environment with the necessary access and configuration. An alert is useful when its recipient, next action and escalation path are clear. After service returns, incomplete requests and data discrepancies still need attention. Together, these decisions and exercises make recovery an operational process with clear responsibilities.
Connecting assets, risk and information-security workflows
Another part of this experience is the standards and information-security management platform developed in Solar Hijri year 1402 for Permon Information Technology. Based on the ISO 27000 family, the application connects assets, vulnerabilities, threats and incidents with risk assessment and related actions. Policies, procedures, forms and records sit alongside audits, corrective actions and effectiveness reviews. For this discussion, the significance of the project is the translation of a management process into traceable software: information needs context, actions need defined responsibility, and reports need a clear meaning for the people making decisions.
How this experience informs our current work
Tiva Safe’s current services focus on business analysis, software architecture, bespoke platforms, systems integration, modernisation and continuous development. Information security, penetration testing and server hardening are no longer offered as standalone services. The experience continues to inform our design perspective: user permissions, data sensitivity, event records, backup arrangements and operational responsibilities should be defined according to each project’s scope. The historical Kerman engagement and the standards-management software project illustrate two different aspects of that experience. Our current standards and organisational-workflow solution describes the software-development direction we now offer in this area.